


Introduction
Imagine your customer database is down on a Monday morning. You cannot get into your emails or files, and your customers are asking when it will be resolved. Whilst you wait for your IT department to resolve the issue, you cannot give any hint at how long you think it will be.
This is becoming a real concern for businesses. A cyber incident can cause problems with orders, services, expose customer data, and ultimately impact your bottom line. It can also cause issues with your trust as well.
In 2026, the threat landscape is evolving. We are using more AI within our day-to-day processes; we are becoming increasingly reliant on third-party platforms, and attackers are looking for new ways to attack US.
From a financial perspective, it can be hard to ignore. IBM found that the global average cost of a breach has increased to US$4.99M (Cost of a Data Breach Report 2026). The World Economic Forum found that 87% of those surveyed felt that AI-based vulnerabilities were the fastest-growing threat to their cybersecurity (Global Cybersecurity Outlook 2026).
You don’t need to invest in every new security tool, but you do need to understand where the vulnerabilities within your business are, what risk is important to you, and how confident you are that you can handle any issues. This should be discussed in your boardroom.
What this guide covers
There are nine sections, and they follow a similar structure: What’s changing? Why does it matter to me? What should I be asking my tech team?
- Cybersecurity needs a place in business decisions
- Software updates and known weaknesses
- AI at work
- Accounts and access
- Suppliers and outside providers
- Backups and recovery
- Cyber fraud and payment checks
- Quantum computing and encryption
- Incident response and reporting

Sources: IBM, Cost of a Data Breach Report 2026; World Economic Forum, Global Cybersecurity Outlook 2026; Verizon, 2026 Data Breach Investigations Report.
The numbers behind this guide
| Measure | What the 2026 reports found | Reference |
|---|---|---|
| Global average breach cost | US$4.99 million, a 12% increase on the previous year | 1 |
| AI-related vulnerabilities | 87% of surveyed respondents called them the fastest-growing cyber risk | 4 |
| Vulnerability exploitation | 31% of initial access vectors in Verizon’s dataset | 3 |
| Third-party involvement | 48% of breaches in Verizon’s dataset | 3 |
| Ransomware | 48% of breaches; 69% of victims in the analysed cases did not pay | 3 |
| Cyber-enabled fraud | 73% said they or someone in their network had experienced it in 2025 | 4 |
1. Cybersecurity Needs a Place in Business Decisions
Security can often be a touchy subject when thinking about software, budgeting for IT, or technical issues.
Take, for example, a business offering an online ordering system. If this system were to go down for 2 days, you would have issues across your entire business. No sales, overload on your support team, and an impact on delivery times. This could cost you far more than just fixing the issue.
It is vital to understand what your key digital assets are as a leader. Not all systems will pose the same risk. Whilst internal systems could cause some frustration, losing customer data or payment systems can cause real issues.
| System (illustrative) | If it stopped for two days | Who feels it first |
|---|---|---|
| Online ordering platform | Sales stop; orders and delivery commitments slip | Customers, sales, fulfilment |
| Customer database | Support cannot look up accounts or history | Support, account managers |
| Payment systems | Cannot take or reconcile payments | Finance, customers |
| Low-risk internal tool | Inconvenient, with workarounds | A single team |
This table is an illustration of how to think about impact, not research data.
Instead of asking if your business is using enough security software, think about what you are trying to protect and why. The NIST Cybersecurity Framework 2.0 provides a similar approach by placing governance (strategy, roles, oversight) at the heart of it all.
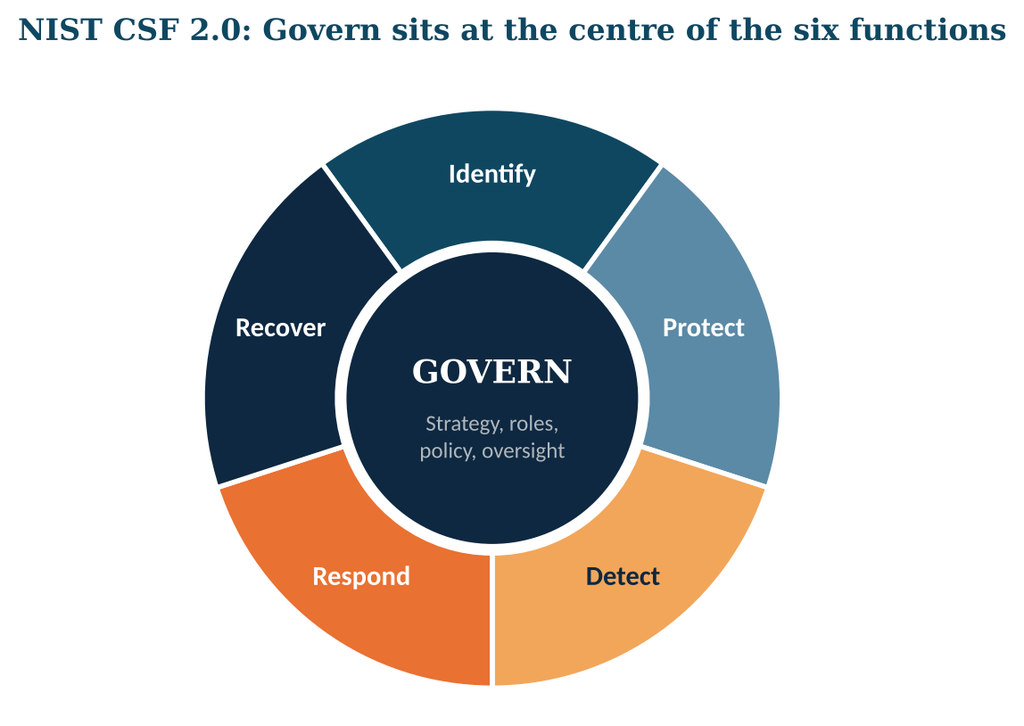
Source: NIST, Cybersecurity Framework 2.0 (reference 5).
Questions to ask your tech team
- Which systems would lead to the biggest disruption if they failed?
- Where is our most sensitive data and information held?
- What are the security threats that need managing?
- Who is responsible for ensuring they are managed?
Any answers should be clear to non-engineers. If you’re giving answers in technical documents, then ask for them to be given in simple terms. You can make security decisions much more valuable by linking them to business outcomes.
2. A Delayed Software Update Can Become a Much Bigger Problem
It can be tempting not to update systems. Teams can get very busy with releases, and developers will want to spend their time testing. This can make updating seem like you’re not really gaining much.
Security patches are much different from feature updates. They often fix known issues.
In the 2026 Data Breach Investigations Report by Verizon, it was found that 31% of access vectors exploited weaknesses within their dataset. If there is a weakness within an exposed application or old system, then the attacker has all they need to gain access.
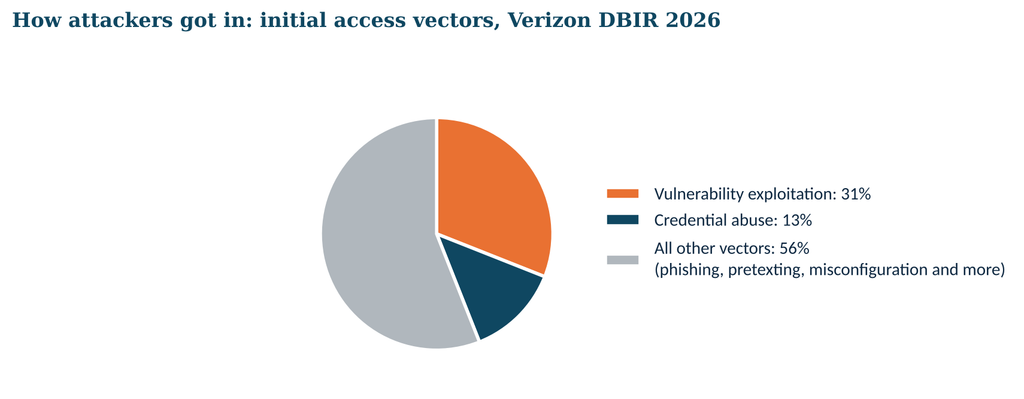
Source: Verizon, 2026 Data Breach Investigations Report (reference 3). The 56% segment is the remainder after the two named vectors and groups all other methods.
This does not mean all updates should be implemented blindly. A sensible approach would consider the severity of the vulnerability itself, how exposed the system is to the internet, and how much reliance you have on your system.
| Situation | How urgently it should be handled |
|---|---|
| Unpatched weakness in an internet-facing customer portal | Needs immediate attention |
| Update to a low-risk internal application | Can follow a different, more routine schedule |
| A weakness that cannot be fixed straight away | Needs a plan for what protects it in the meantime |
Questions to ask your tech team
- How do you identify and prioritise vulnerabilities?
- Is there a system inventory, and do you monitor when patches are overdue?
- What is your process for identifying weaknesses that can’t be resolved immediately?
It’s important to know that the updates are being applied in a way that ensures the most dangerous gaps are not left open.
3. AI Brings Opportunities and New Security Questions
We’re seeing people using AI in ways that help them in their work. Whether they’re asking for document summarisation, coding, drafting responses to customers, or analysing information. Businesses are also introducing AI-enabled apps and integrating them into their systems.
This can be seen to improve productivity; however, there are less obvious security implications.
| What happens | What can go wrong | A sensible boundary |
|---|---|---|
| An employee pastes a confidential customer document into an unapproved AI tool | Information leaves the organisation without anyone intending it | A clear list of approved tools and what may be shared |
| An AI assistant is connected to internal systems | It may reach more data than it needs | Developers review the permissions each application gets |
| An AI answer looks convincing but is wrong | Bad information feeds an important decision | Human oversight on decisions that matter |
Attackers are also using AI to increase the realism of scams and malicious attacks. On average, they cost around US$6 million to breach. IBM’s research shows that 1 in 4 malicious breaches can be tied back to AI. The World Economic Forum’s report on 2026’s outlook shows that respondents are growing increasingly worried about vulnerabilities that could come from AI.
You won’t be able to completely stop people from using AI, but you should understand how it is being used. Controls will be needed.
Questions to ask your tech team
- Do you know what AI tools your staff are using?
- Where does the data go?
- Can your AI applications access internal data and act on behalf of users?
- Is there any validation of AI-generated data before being used to make important decisions?
The adoption of AI will continue to rise. Those who can get the most out of it will be those who ensure security is integrated from the start.
4. Protecting Accounts Matters as Much as Protecting Systems
Even with firewalls, endpoint security, and monitoring in place, a company can still suffer greatly if an attacker gains entry to one legitimate user account.
This is why credential theft, phishing, and spoofing are of great concern. Attackers may attempt to persuade employees to give away their passwords, approve logins, or transfer money to fake accounts.
Two credential figures that are easy to mix up
Verizon’s 2026 report shows that 13% of initial access cases in their report involved compromised credentials, and overall 39% of cases involved compromised credentials throughout the breach lifecycle. These are separate values.
| What is being measured | Figure | What it tells you |
|---|---|---|
| Credential abuse as an initial access vector | 13% | How often stolen or misused logins were the way in |
| Credential abuse across the wider breach progression | 39% | How often credentials played a part at any stage of a breach |
Source: Verizon, 2026 Data Breach Investigations Report (reference 3).
Multi-factor authentication can be used to help secure these systems, especially administrator systems, remote systems, and any systems that contain sensitive data. Access controls should also be regularly reviewed to ensure users no longer have unnecessary access after changing roles or leaving the company.
Social engineering attacks are often more successful than technical attacks. These can include things like pretending to be your manager and asking you to make an urgent payment. It is important to educate users to always be suspicious if they are being asked to do anything unusual.
What to review
- How you grant, modify, and revoke access to accounts
- Are suspicious logins being monitored?
- Is multi-factor authentication available for administrators, remote access, and sensitive systems?
- Do staff receive training to help them identify impersonation?
This makes it more difficult for attackers to exploit the account and allows any employees to question anything they do not feel comfortable with.
5. Your Suppliers Can Affect Your Security
Most businesses won’t be purely operating on their own tech stack. You will be using a range of different services such as hosting, cloud, payment, software, agencies, etc. This increases the security scope.
If one of these vendors has access to your systems, customer information, or internal applications, they could cause some impact if there is an incident. A study by Verizon showed that 48% of breaches within their data set had third-party involvement (Verizon, 2026).

Source: Verizon, 2026 Data Breach Investigations Report (reference 3). Each measure has a different base, so compare them with care.
It’s not that you shouldn’t use third-party suppliers, but to better understand how much access they will have and the processes they will undertake. If your supplier has access to sensitive customer information, you will clearly know a lot more about their processes than you would if you had no access to your internal systems.
Questions to ask before and during a supplier relationship
- What information or systems does the provider have access to?
- Is it limited to what they require?
- Are security responsibilities defined within the contract, including how and when incidents will be reported?
- How regularly are our key suppliers reviewed?
- What is the contingency plan if we lose a key provider?
Supplier security is not a one-time activity. As relationships change along with your permissions and dependencies, you will need to regularly review your supplier security.

6. Backups Only Help If the Business Can Recover
Ransomware can cause huge problems for organisations as it can keep users locked out of their systems and data. Attackers can also seize information and threaten to publish it.
Verizon found in 2026 that 48% of breaches included ransomware and 69% of victims did not pay the ransom. As a leader, this means that you shouldn’t rely on your ability to negotiate with attackers.

Source: Verizon, 2026 Data Breach Investigations Report (reference 3). The 31% segment is the remainder.
Most organisations know that having a backup is important but can struggle to determine how effective it will be. If a backup has not been tested, it could be incomplete or have been stored in the same compromised environment as the original data, causing it to be impacted.
Questions to ask your tech team
- When did we last restore critical systems as a test?
- How long would it take to bring essential services back?
- Could the business keep operating in the meantime?
What a realistic recovery plan covers
- Which services must come back first
- Who makes recovery decisions
- How employees and customers will be told
- What temporary arrangements are available
The aim here is to ensure that your business does not grind to a halt due to one incident.
7. Cyber Fraud Is Not Always a Technical Attack
Many of the worst impacts happen after a seemingly normal email, phone call, or payment request. This can include receiving an invoice from a trusted supplier. Someone in your finance department will be asked to change bank details, or staff will receive a message from what seems like their director asking for an urgent payment.
These can be very hard to identify as they exploit human error and trust.
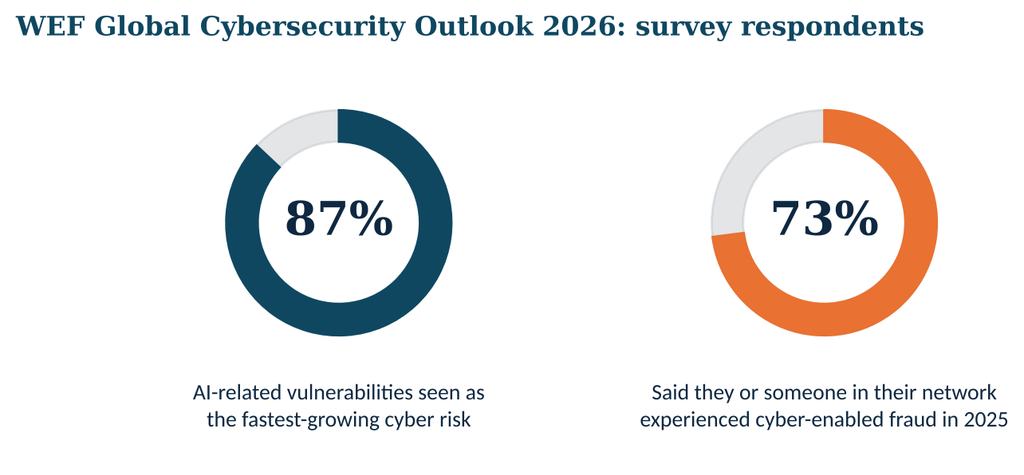
Source: World Economic Forum, Global Cybersecurity Outlook 2026 (reference 4). The 73% figure is a survey finding about personal or network exposure to cyber-enabled fraud in 2025. It is not a measure of how many companies suffer data breaches.
Ensuring that payment verification becomes a standard process, with each member of the team (Finance, HR, Management, IT) playing their part.
| If you see this | Do this first |
|---|---|
| A request to change a supplier’s bank details | Confirm it through a trusted contact method, not by replying to the email that asked for the change |
| An unusual payment that is marked urgent | Follow the approval procedure, however pressing the request seems |
| A message that appears to come from a senior leader | Verify it, even when it looks genuine |
| Anything that feels off | Report it. Employees should know exactly where |
With managers setting the example to show that adhering to the verification processes is more important than appearing rushed.
8. Quantum Computing Is a Future Risk Worth Preparing For
Whilst this may not be an issue for most companies, if you handle sensitive information, then you might want to think about how post-quantum cryptography will affect you.
Many common public-key cryptographic systems are vulnerable to quantum computers powerful enough to break them. There are also issues with adversaries storing encrypted data and trying to break it.
The NIST has already published 3 post-quantum crypto standards:
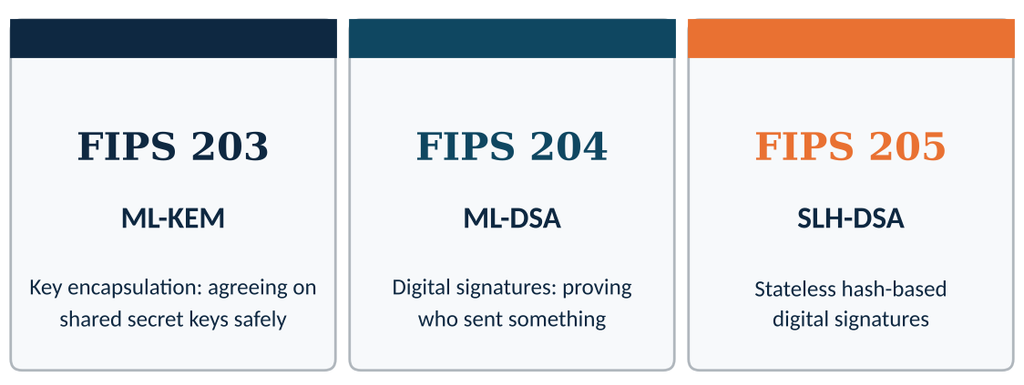
Source: NIST, Post-Quantum Cryptography Standards (reference 6).
This doesn’t necessarily mean that every organisation has to migrate its encryption methods, but it is about understanding where you are using cryptography, what data needs to be protected for the long term, and if your technology providers have a transition strategy. If you’re in the finance, healthcare, government services or research sectors, you may have more of a reason to think about this sooner.
A good starting point would be using the NIST transition guidance document (NIST IR 8547). Please note that the transition timelines for federal systems may not necessarily apply to private organisations.
Questions to ask your tech team
- Where are you using cryptographic technologies?
- Which information do you need to protect for a long time?
- Do your key technology partners have any plans for moving to post-quantum?
9. A Response Plan Matters Before an Incident Happens
Even the most secure of organisations can experience problems. Having a plan can help you have a significant impact on the event. Without knowing who should make decisions, interact with customers, and report to regulators, you will waste time.
A good incident response plan will outline who should do what and bring everyone that may be involved together (technology, management, legal, comms, HR, business).
Reporting requirements differ by place
The rules depend on where you operate, what information is involved, and which regulations apply. These are general summaries, not legal advice.
| Region or rule | What generally applies | Worth remembering |
|---|---|---|
| United States (SEC) | Companies under the SEC’s cybersecurity disclosure rules generally file Form 8-K within four business days after determining an incident is material | The period doesn’t automatically start when the incident is first discovered |
| European Union (NIS2) | Early warning within 24 hours, incident notification within 72 hours, and a final report generally within one month | Applies to covered entities |
| India (DPDP Rules, 2025) | Affected individuals must be informed without delay. The Data Protection Board must also be notified without delay, with detailed information generally within 72 hours | Subject to applicable provisions and commencement dates |
| India (CERT-In directions) | Specified reportable incidents must be reported within six hours of noticing them or being brought to notice | Not a requirement to report every routine security alert |
Sources: SEC, Cybersecurity Risk Management, Strategy, Governance, and Incident Disclosure (8); NIS2 Directive (9); DPDP Rules, 2025 (10); CERT-In Directions (11). Confirm current requirements with qualified advisers.
Test the plan with a simple exercise
An easy way to test your preparedness is to run a brief incident simulation. Provide the team with a realistic scenario (e.g., an employee account has been breached, or a customer database is down). This will often highlight communication, decision-making, or recovery issues that the policy document may not have identified.
Your Question Checklist at a Glance
One page that I would encourage you to refer to during your next meeting with your tech team is this one. The third column shows you what a confident and specific answer tends to look like.
| Area | The question to ask | A strong answer sounds like |
|---|---|---|
| Business impact | Which systems would hurt most if they stopped? | A named, ranked list tied to revenue and customers |
| Updates | How do we prioritise and track vulnerabilities? | Exposed systems first, overdue patches tracked, exceptions explained |
| AI | Which AI tools are in use, and what data goes into them? | An approved list, clear rules and a way to spot tools outside it |
| Accounts | Where is multifactor authentication enforced? | Administrators, remote access and sensitive systems, with leavers removed promptly |
| Suppliers | What can each key provider access? | Access limited to need, contract terms on incident reporting, regular reviews |
| Recovery | When did we last restore from backup? | A recent test, a time estimate and a list of what returns first |
| Fraud | How are bank-detail changes verified? | A second, trusted channel every time, whoever is asking |
| Quantum | Where do we use cryptography? | An early inventory and a view on provider migration plans |
| Response | Who decides and who reports? | Named people, tested in an exercise, aware of the clocks that apply |
The right-hand column is a practical suggestion for judging answers, not a finding from the cited reports.
What Should Leadership Review Regularly?
You don’t need to give a lengthy presentation. Senior management just want to know that the major risks are being addressed. So maybe have a discussion once per quarter on the following points:
| Area | What leadership should understand |
|---|---|
| Vulnerabilities | Are critical weaknesses being resolved on time? |
| Account security | Are MFA and appropriate access controls in place? |
| Backups | Have important systems been restored successfully in tests? |
| Suppliers | Are high-risk providers being reviewed? |
| Employee awareness | Do employees know how to recognise and report suspicious activity? |
| Incident readiness | Does everyone know their role during a security incident? |
| AI use | Are approved tools and data-access rules being followed? |
Keep it to the key points and keep it simple. Don’t give a long list of technical issues. Focus on the issues that have changed, are in question, and require management support. Clearly outline the risk to the business.
Where Should Businesses Start?
Trying to do all of this at once can be a bit much to take in. Focus on the most important gaps to close in the next 3 months.
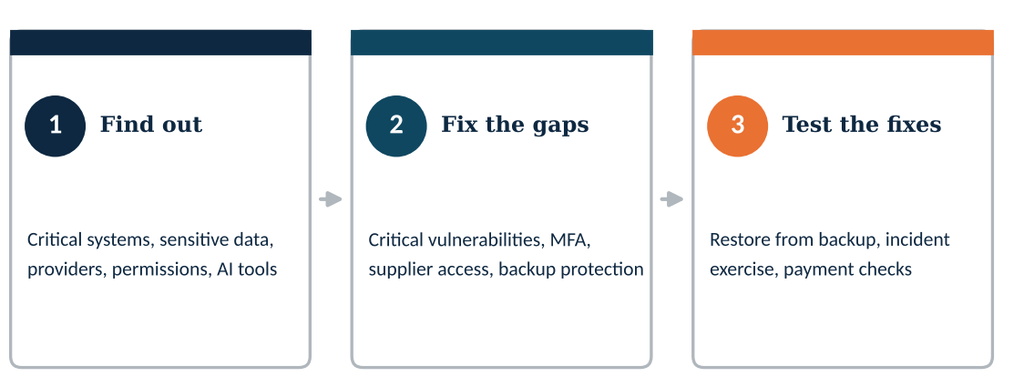
Month 1: find out where you stand
Find out the main systems, sensitive information, third parties, and areas that are vulnerable. Audit the access controls and see how many AI tools are being used.
Month 2: fix the gaps that could do the most harm
Fix any critical vulnerabilities. Get MFA working well. Audit third-party access. Make sure backups are secure.
Month 3: check that the fixes work
Do some backup restore testing on the key data. Run through the incident response plan. Audit the payment validation process. Make sure you know who would raise any security incidents.
Overall, the leaders will have a greater knowledge of the risks your organisation has, what has been done and what needs to be looked at.
Conclusion
Cybersecurity is generally viewed as a technical aspect but can affect the entire business. If an account is compromised, you may have issues with customers. If there is an issue with a supplier, this can cause disruption. Ransomware can mean people cannot complete their tasks.
Leaders should get involved. You do not need to know everything about the tools and configuration, but it is important to know what is most important to protect, who is responsible, and if you are prepared to recover from an incident.
The most useful conversation you can have with your tech team is:
- What is the biggest threat to your business?
- If there were a significant incident tomorrow, how will you continue to operate?
- What must change, and what do you need from leadership?
They provide clear answers and are a much better place to start than looking at adding another security solution.
Protect Your Business from Emerging Cyber Threats

Pooja Upadhyay
Director Of People Operations & Client Relations
References
https://www.ibm.com/reports/data-breach
https://www.verizon.com/business/resources/reports/dbir
https://www.weforum.org/publications/global-cybersecurity-outlook-2026
https://www.nist.gov/cyberframework
https://csrc.nist.gov/projects/post-quantum-cryptography
https://csrc.nist.gov/pubs/ir/8547/final
https://eur-lex.europa.eu/eli/dir/2022/2555/oj
https://www.cert-in.org.in/PDF/CERT-In_Directions_70B_28.04.2022.pdf
